Golden Dragon OS & Verifier
Operational security
for high-stakes operations.
Hardened laptops, auditable, amnesic OS, and supply-chain-verified USBs
so executives sleep better.
bernard.labno@goldendragon.pt
jg@goldendragon.pt
For review · 2026-04-29
Why we're here
We built this for ourselves.
Jason saw it last week and thought you should see it too.
Today is not a pitch for a check.
We have funds for development, audit, and pentest. What we want from you is the thing nobody else in our network can give us:
Let me show you the actual thing first — much faster than describing it.
OS demo
Stop sharing this deck → switch to camera with the boot USB → screen-share VirtualBox at BIOS prompt → resume → Plymouth → desktop → Firefox tabs → facebook.com blocked → KeePassXC → eject → narrate RAM scrub.
When done, return to the deck and continue from slide 3.
The trust gap
$1.5 billion stolen through a compromised laptop.
Bybit, February 2025. Not the exchange. Not the wallet. The operator's endpoint.
Where the industry has invested
- Hardware wallets — solve cold custody
- Multi-sig & MPC — solve key splitting
- Fireblocks & institutional custody — solve operational policy
- Exchange security — solve their side
Where it hasn't
- The operator's terminal.
- Persistent OS = monotonically growing attack surface.
- One phish, one driver bug, one cleaner — and the keys are theirs.
- Hardware wallets don't help if the laptop signs the wrong tx.
What you just saw is our answer.
Defense in depth
Six independent layers. Every one fails closed.
NovaCustom V54, Dasharo coreboot, camera/mic removed, tamper-evident
Verifier device cryptographically checks USB before every boot
Read-only image, RAM-only state, scrubbed on shutdown
nftables outbound HTTPS only; no inbound; no Tor
Firefox policy with GPG-signed exchange allowlist
Per-operator LUKS2 credentials USB
An attacker has to defeat every layer to compromise a session. Most existing crypto-fund setups have one or two of these. None we've seen has all six.
There's a question that follows the demo
How do you know the USB on your desk is the OS we built?
Any auditor can rebuild it from source. We verify the bytes we publish.
Someone with five minutes of physical access — a cleaner, a hotel maid, a curious colleague — can swap, modify, or implant.
There is a second device for that.
The verifier — hardware
Pi Zero. Two USBs. One LED.
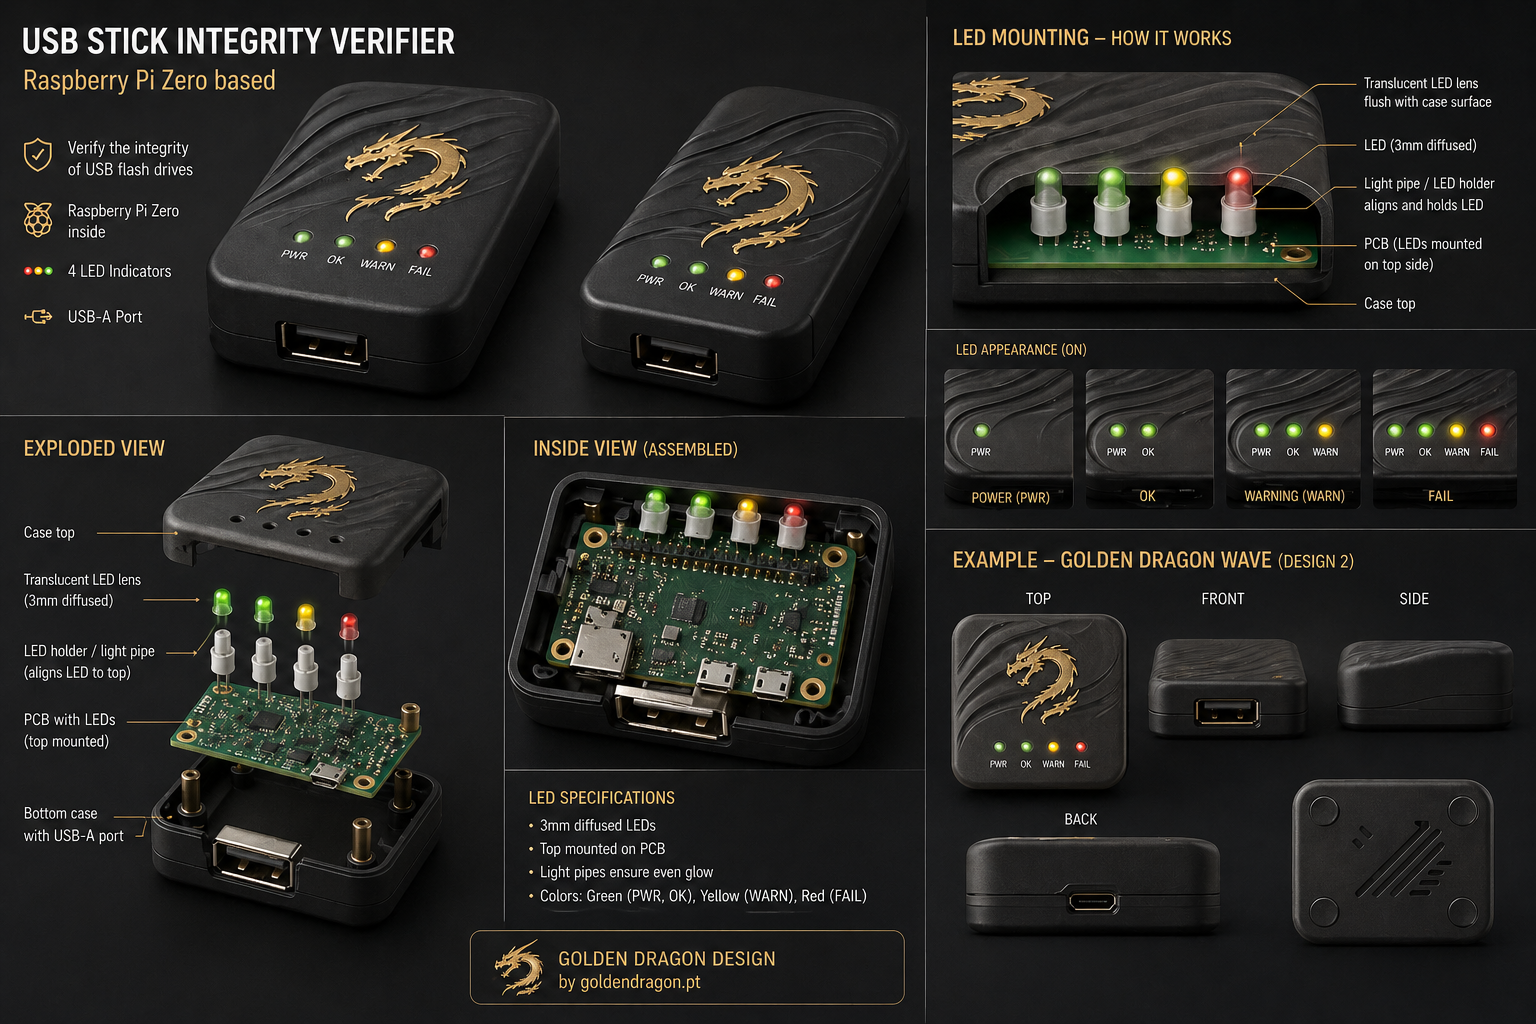
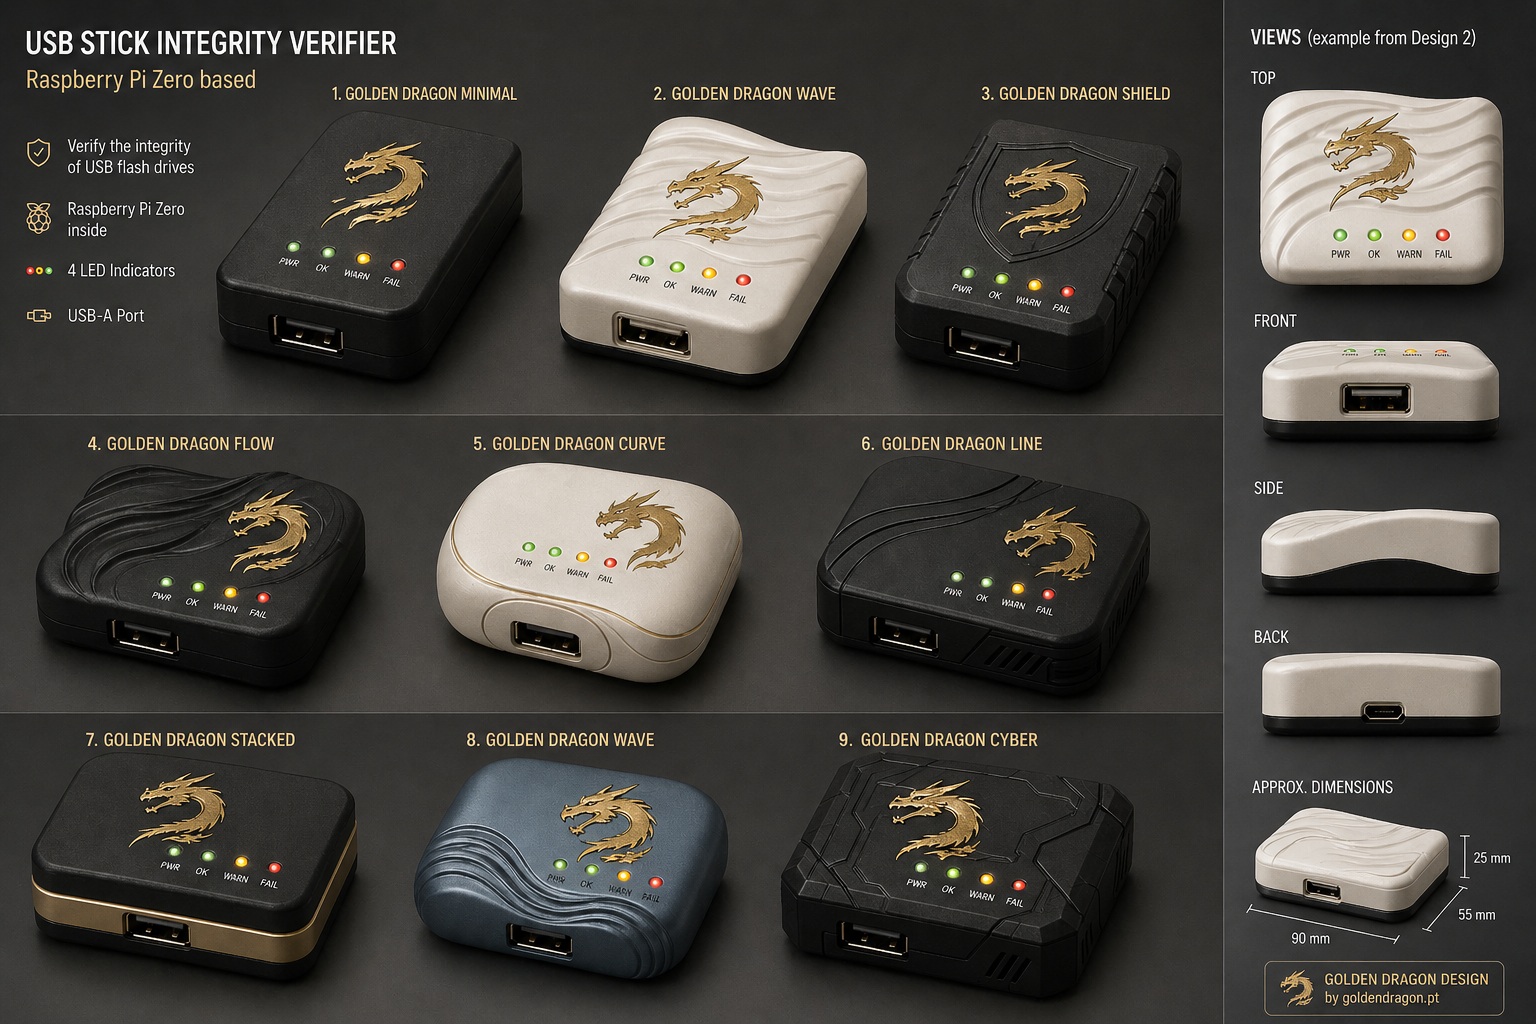
No WiFi. No Bluetooth. Boot USB and Manifest USB go in; the LED reports green or red. Final assembly is waiting on a USB connector batch before live verification — video of the green/red flow follows the moment that ships.
Verifier trust chain
Notary-grade separation of duties.
Signing & verification chain
Cross-check social trust
Each trader has a personal Pi. Compromising one trader requires compromising both their USB and their Pi and hoping no colleague double-checks.
Built to be audited & adapted
Three things that turn this from a product into infrastructure.
01 / Auditable
Reproducible buildsAny auditor rebuilds the ISO from source — bit-for-bit identical to the distributed image. 13 architecture decision records. Living spec. Builds from versioned code, not manual steps.
"Most security products are a black box. Ours isn't."
02 / Adaptable
Customizable per clientCode is the source of truth. Custom builds per fund — your exchange allowlist, your branding, your hardware spec. Source license available — your team can take customization fully in-house. Verifier signing stays with us: the trust anchor doesn't move.
"You're not buying a SKU. You're buying a platform."
03 / Durable
Not a startup-bus-factor riskVersioned, documented, reproducible. If we disappear tomorrow, throw the verifier away — your team keeps building and deploying custom ISOs. Enterprises hate small-vendor lock-in; this neutralizes it.
"You'll keep operating even if we don't."
Each pillar lands a different objection: auditability for the CISO, adaptability for ops, durability for procurement.
Where else this lives
Crypto is the urgent vertical. The threat model isn't crypto-specific.
Today — beachhead
Crypto funds & family officesWhere the urgency is hottest — Bybit forced everyone to look hard at the signing endpoint — and where we're moving onto it ourselves first.
Next 18-36 months — adjacent
Banking ops · securities trading · private wealthSame threat model: a single endpoint compromise can mean catastrophic loss. Same defense-in-depth answer. Different sales motion, different compliance overlay.
★ The whole reason for this conversation
What we want from you.
Three questions. Honest answers more valuable than a check.
Would your fund — or your family office, or your client — actually use this? At what price?
Who in your network do you think needs this?
What's missing? What objection have we not anticipated?
Thank you
That's the whole story.
We'll send a follow-up within 24 hours with:
- This deck as PDF
- A short one-pager you can share without context